How ServiceRocket Runs a Year-Round SOC 2 and ISO 27001 Program

Insight Assurance and ServiceRocket logos on the ServiceRocket SOC 2 and ISO 27001 case study card
About ServiceRocket

At a glance

ServiceRocket, a Palo Alto tech-enabled services company focused on the Atlassian suite, holds a SOC 2 Type II report from an examination by Insight Assurance and ISO 27001 certification issued through IA Certifications. Its GRC team keeps the program current year-round in Vanta. Enterprise clients now often accept the reports instead of lengthy security questionnaires.

  • Client: ServiceRocket, a tech-enabled services company (Atlassian consulting, support and licensing), about 260 personnel in seven countries
  • Frameworks: SOC 2 Type II and ISO/IEC 27001
  • What they needed: Credible third-party evidence to replace lengthy enterprise security questionnaires
  • What Insight Assurance did: Conducted the SOC 2 Type II examination; ISO 27001 certification issued through IA Certifications
  • Result: Enterprise clients often skip questionnaires; Catherine Matterson rated the experience 10 out of 10

ServiceRocket is a tech-enabled services company headquartered in Palo Alto, California, with approximately 260 personnel including employees and contractors across seven countries. The company provides consulting, support services, and license resales primarily around the Atlassian suite of products, serving enterprise clients across Australia, the United States, and beyond.

With a global footprint and enterprise client base, ServiceRocket operates in an environment where security and data protection are commercial prerequisites. Enterprise customers regularly ask for third-party validated evidence before beginning a working relationship, and the ability to produce it quickly and credibly directly affects how deals move forward.

Today, ServiceRocket holds a SOC 2 (System and Organization Controls 2) Type II report and an ISO 27001 certification for information security management. The SOC 2 examination was conducted by Insight Assurance, and the ISO 27001 certification was issued through IA Certifications, an independently accredited certification body. The company uses Vanta to support its compliance efforts and maintains a dedicated GRC (governance, risk, and compliance) team responsible for keeping its compliance program current year-round.

Insight Assurance spoke with Catherine Matterson, General Counsel at ServiceRocket, who heads the legal team and shares responsibility for the company’s security certifications and data compliance program. Catherine has been with ServiceRocket for 13 years.
The Challenge

ServiceRocket’s compliance journey was driven by a clear and direct signal from the market.

  1. As the company’s enterprise client base grew, customers began sending lengthy security questionnaires before onboarding. The volume and complexity of those requests made it clear that a questionnaire-based approach was no longer sustainable. “It’s easy enough to fill in a questionnaire,” Catherine explained, “but if you can actually provide a very credible, third-party certification, obviously a lot of weight attaches to that.
  2. Operating across seven countries, with an IT team based primarily in Malaysia and leadership in both Australia and the United States, managing compliance across time zones and jurisdictions added operational complexity to what was already a demanding process.
  3. Each framework the program took on, whether SOC 2 or ISO 27001, required a more structured internal foundation, including policies, roles, testing, and evidence, that ServiceRocket had to build deliberately and maintain continuously. “It’s not a rubber stamp,” Catherine noted. “You actually have to enact what’s in there and make sure people are following it.”

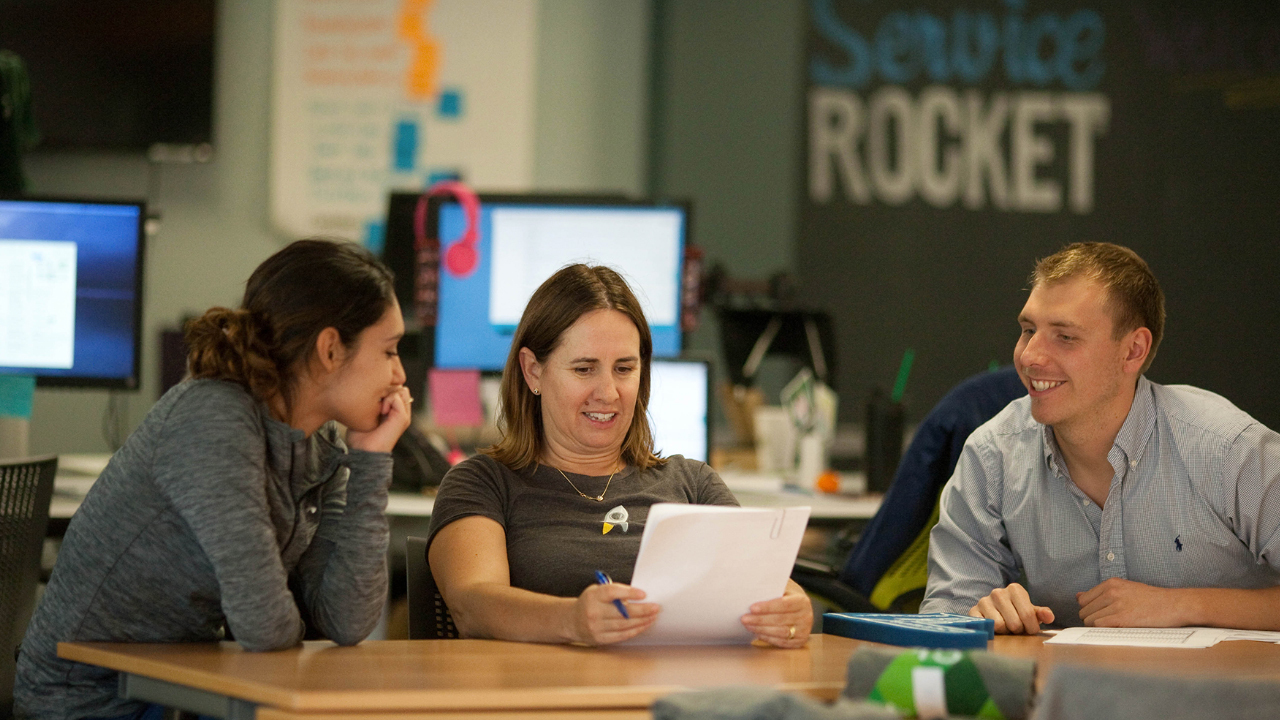
ServiceRocket team

The Solution

ServiceRocket came to Insight Assurance through a referral, seeking an auditor with direct experience in American technology companies that could work effectively across time zones.

The compliance program itself runs on a structured monthly cadence. Catherine’s GRC team meets regularly to review the risk register, go over policies, and use Vanta’s dashboard to identify what needs attention before the next assessment cycle. “Every month we go in and we just see, OK, where do we need to review and update to be ready for the next audit?” she explained. Ownership and timelines are kept on track through a ticketing system that sends annual reminders for policy reviews.

For the SOC 2 Type II examination, the team found the day-to-day experience with Insight Assurance well organized and responsive. “They really do provide excellent project management,” Catherine said. “There were timely daily debriefs from our auditor with clear summaries, findings, and follow-up items. And then whenever there was any follow-up, usually within 24 hours, we were provided an answer.”

The ISO 27001 engagement brought a different kind of challenge, one that came from ServiceRocket’s side. The team discovered partway through that its internal audit needed to be completed before the Stage 1 audit, which created an unexpected scramble. Catherine was candid about where the issue originated. Insight Assurance clarified the certification body’s requirement, and ServiceRocket completed its internal audit before the audit resumed. Catherine said: “We were really grateful to the team at Insight Assurance for putting us back on track by steering us in the right direction.”

One detail Catherine highlighted as particularly meaningful was a staffing decision Insight Assurance made for the engagement: assigning an auditor based in the Asian time zone. With most of ServiceRocket’s IT team in Malaysia, the alignment made a practical difference. “A lot of times my team would have to get up very early in the morning or late at night. So we very much appreciated that we were provided with an auditor in a time zone that suited the majority of where we were.”

The Results

Since its SOC 2 Type II examination and ISO 27001 certification, ServiceRocket reports several meaningful outcomes:

A Security Culture That Goes Beyond the Audit

Catherine described ServiceRocket’s own internal changes as significant. “We’ve seen a highly disciplined enhancement in our security posture at ServiceRocket.” Taking a proactive stance, the IT team now drives quarterly security checks, regular phishing simulations, and continuous policy reviews. A key outcome of this evolution has been sharper internal clarity: “People’s roles were then clearly defined within those policies. Our personnel now clearly understand all required aspects of their roles”

Compliance That Replaces Questionnaires

Enterprise clients, particularly in Australia and the United States, regularly request the SOC 2 Type II report and ISO 27001 certification before beginning a working relationship. The effect has been a measurable reduction in administrative friction. “Often they will say they don’t need us to fill those lengthy questionnaires,” Catherine noted, “which is always good.”

Beyond time savings, the credentials have also shaped how customers perceive ServiceRocket. “They definitely do trust us more because we obviously spend a lot of time getting these certifications by putting robust security measures in place,” she said. “It has definitely lent itself to people feeling, our customers, I would believe, more secure about who they’re dealing with and the level of security that their data is protected by.”

A 10-Out-Of-10 Engagement

Catherine rated the overall experience a 10 out of 10 and has already recommended Insight Assurance to others. She summed up what she values most about the working relationship: “The expertise and knowledge, they really draw down on us so we know we are putting in place tight security measures. Also, we get really good feedback. There are some fabulous templates that have been developed by Insight Assurance that have been shared with us over the years, that are constantly updated so that we know we’re looking at the latest requirements we need to adhere to.”

She also added something that stood out for its simplicity: “You are very transparent. You have reasonable pricing and it’s just very transparent. I know what I’m getting.”

Conclusion

If you run a global technology services company with enterprise clients, compliance is a program you build, maintain, and improve year over year. ServiceRocket’s experience across multiple SOC 2 and ISO 27001 cycles reflects what that kind of sustained commitment looks like in practice.

With a well-run internal GRC program and a consistent, independent audit relationship, ServiceRocket has made compliance work for the business: in security reviews, in sales conversations, and in the confidence it gives the people doing the work every day.

More Case Studies

Ready for Stress-Free Compliance?

Whether you’re a two-person team or a global enterprise, our team of former Big 4 auditors brings the same level of quality and care to every engagement.

Let’s simplify compliance — together.

Share This Post

Let's Talk Compliance

Share a few details and our team will be in touch shortly to schedule a friendly, no-pressure conversation—no obligations, just answers.

Insight Assurance needs the contact information you provide to us to contact you about our products and services. You may unsubscribe from these communications at any time. For information on how to unsubscribe, as well as our privacy practices and commitment to protecting your privacy, please review our Privacy Policy.