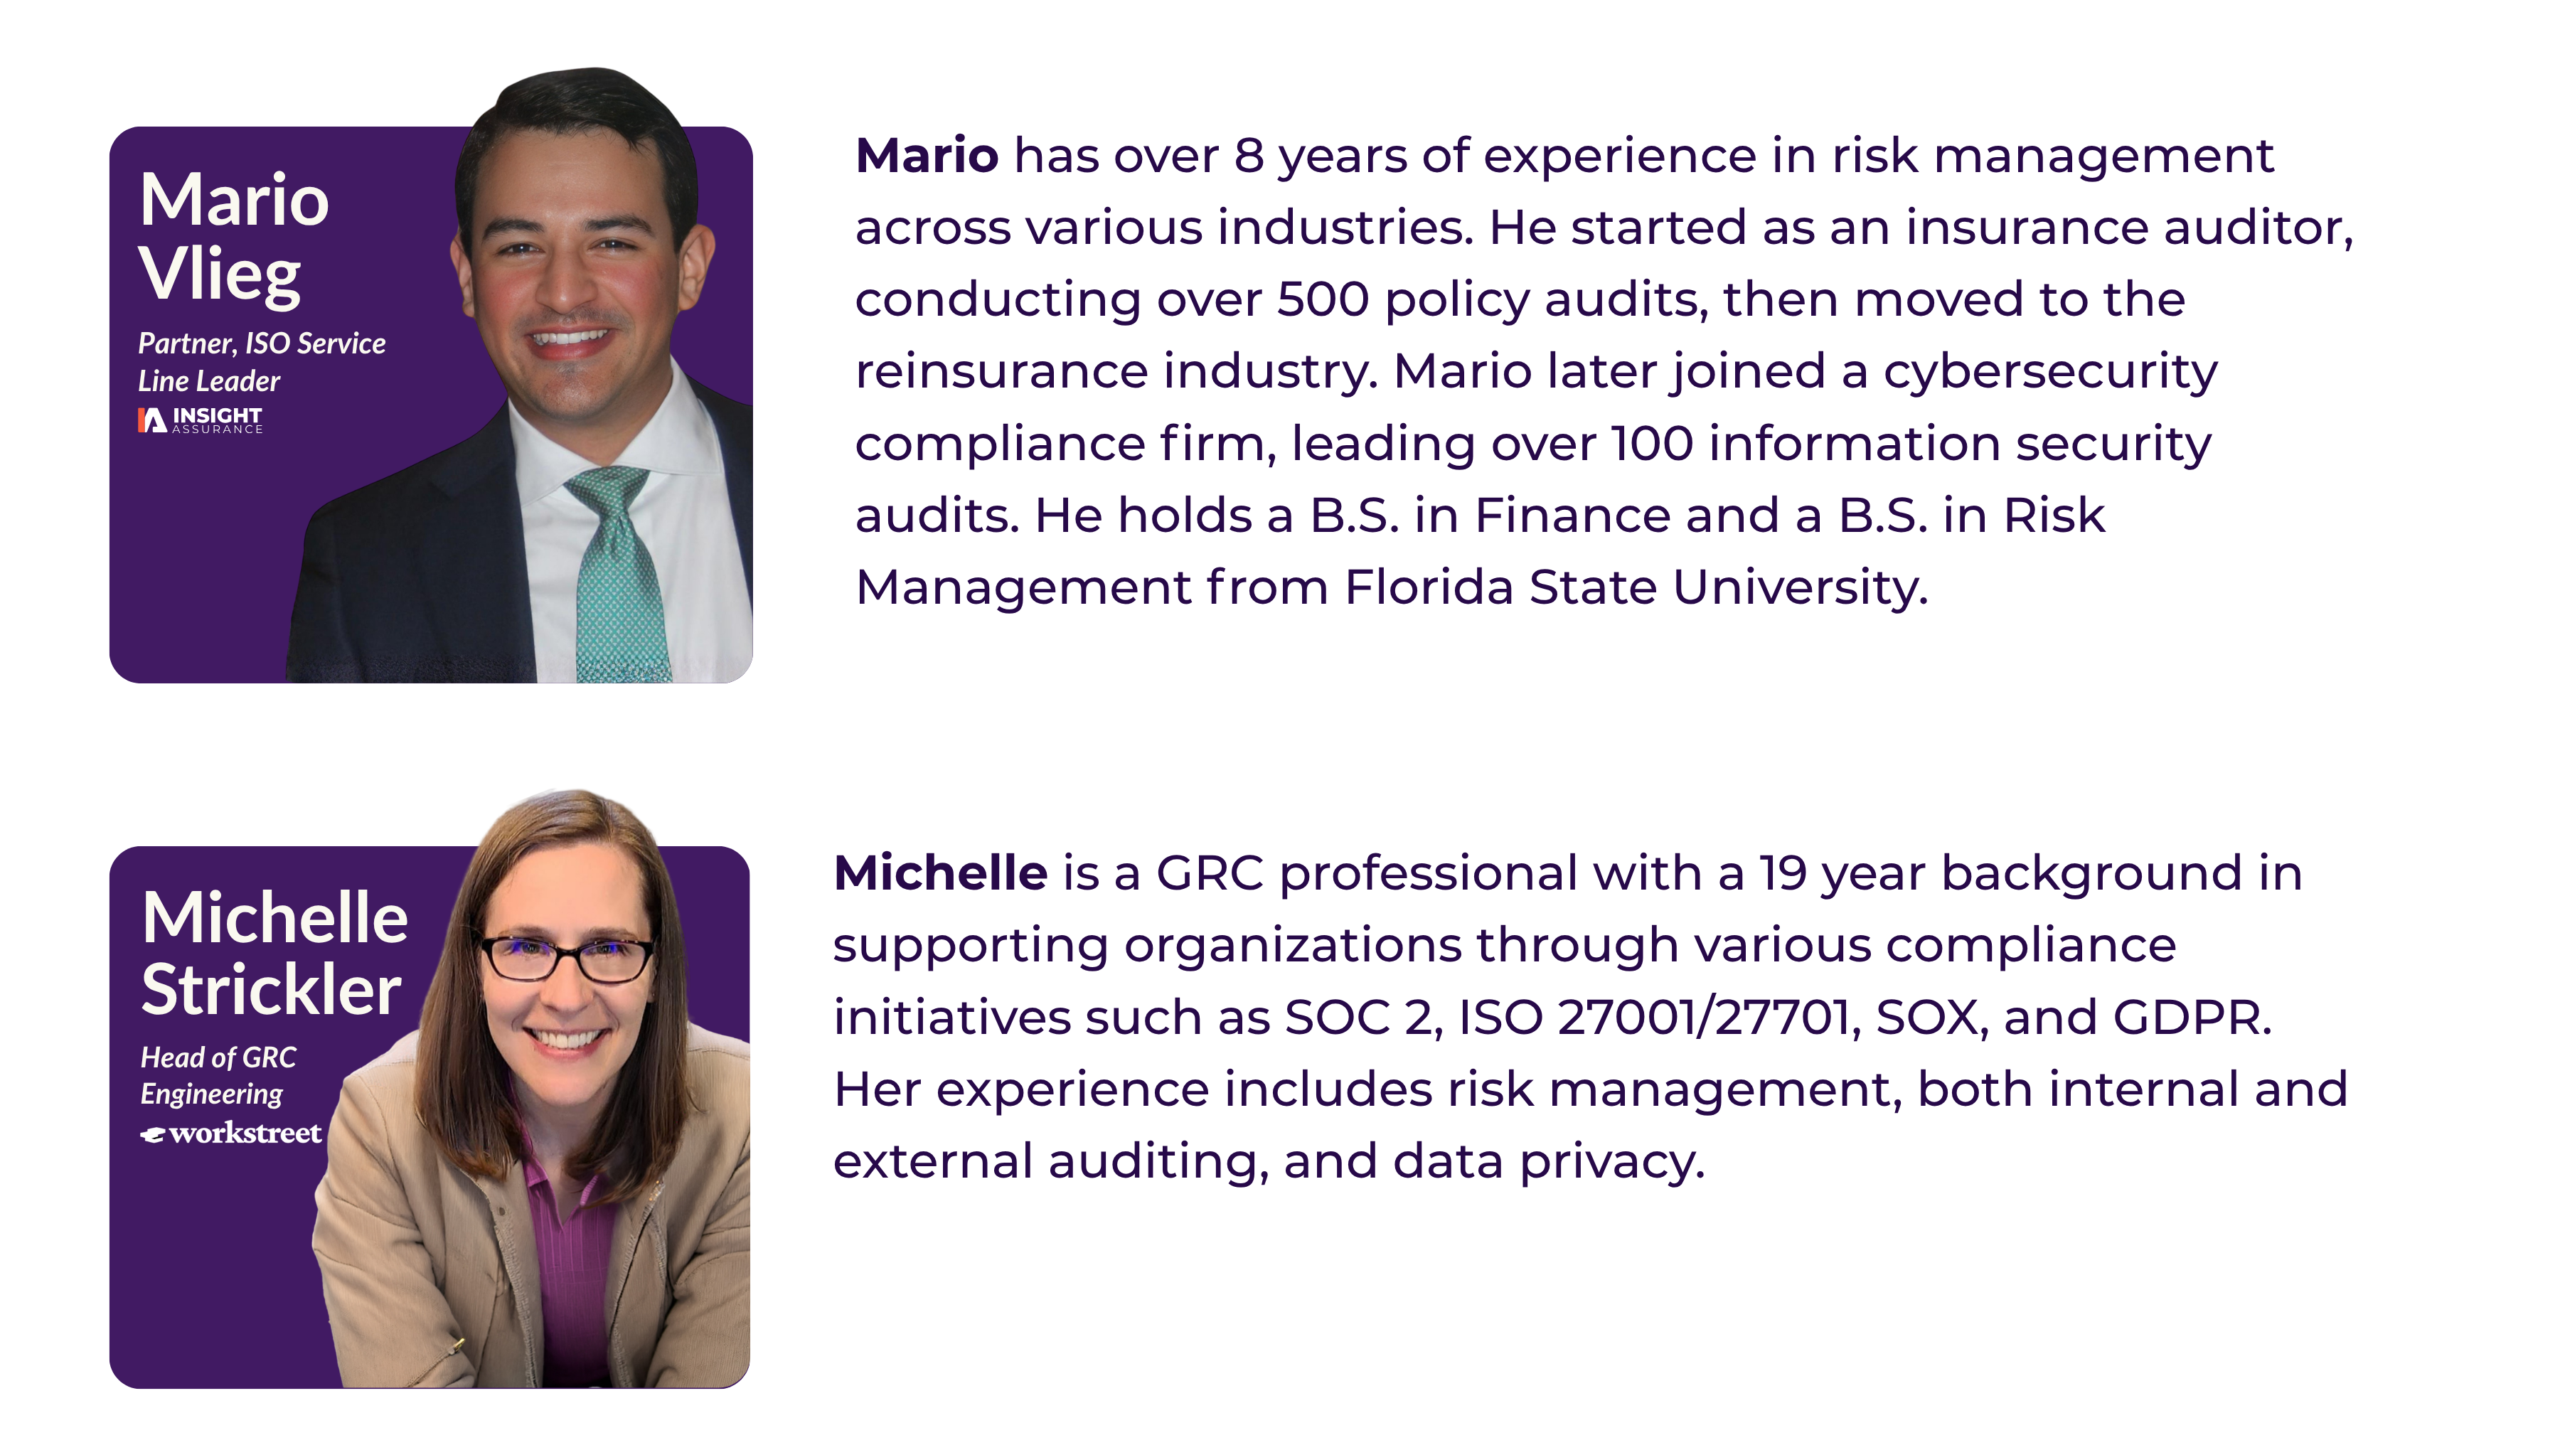
In June 2026, the EU Council pushed back the AI Act’s high-risk compliance deadline, but customers and regulators are still asking for AI governance evidence now. Insight Assurance’s Mario Vlieg sat down with Michelle Strickler, Head of GRC Engineering at WorkStreet, for a vendor-neutral walkthrough of ISO/IEC 42001: what it is, who it applies to, and what happens during an independent assessment.
In this session:
- Did the EU AI Act deadline move? Yes, and we break down what that shift does (and doesn’t) change.
- Do you actually need ISO 42001? Applicability comes down to your role in the AI lifecycle, and we walk through how to figure out which one applies to you.
- How does ISO 42001 relate to ISO 27001 or SOC 2? We cover where the frameworks overlap and where ISO 42001 adds AI-specific requirements.
- What does an assessment actually evaluate? From Stage 1 documentation review through Stage 2 evidence testing and the ongoing certification cycle.
- What’s the difference between getting “audit-ready” and being assessed? WorkStreet and Insight Assurance sit on either side of that line, and we explain both.
Missed it live? Watch the full session now.
Who should watch
Security leaders, compliance managers, and risk professionals at organizations that hold or are pursuing ISO 42001 certification and are beginning to evaluate AI governance.
Speakers